Why Data Protection Matters for Business Analysts?
As a Business Analyst (BA), I think our job goes beyond defining what a system should do. We also need to consider how data is collected, accessed, stored and managed throughout its lifecycle.
I feel that privacy becomes much harder to manage when it is treated as a last-minute compliance task. For example, if access permissions are not defined during design, the team may build broader access than necessary, and fixing it later means changing application logic, database permissions and tests.
And I have come to realise that the questions we ask during requirement gathering shape how responsibly a system handles personal data. The principle is simple: collect only what is necessary, protect what is collected, and set clear rules for how it is used.
The 5-Step Framework
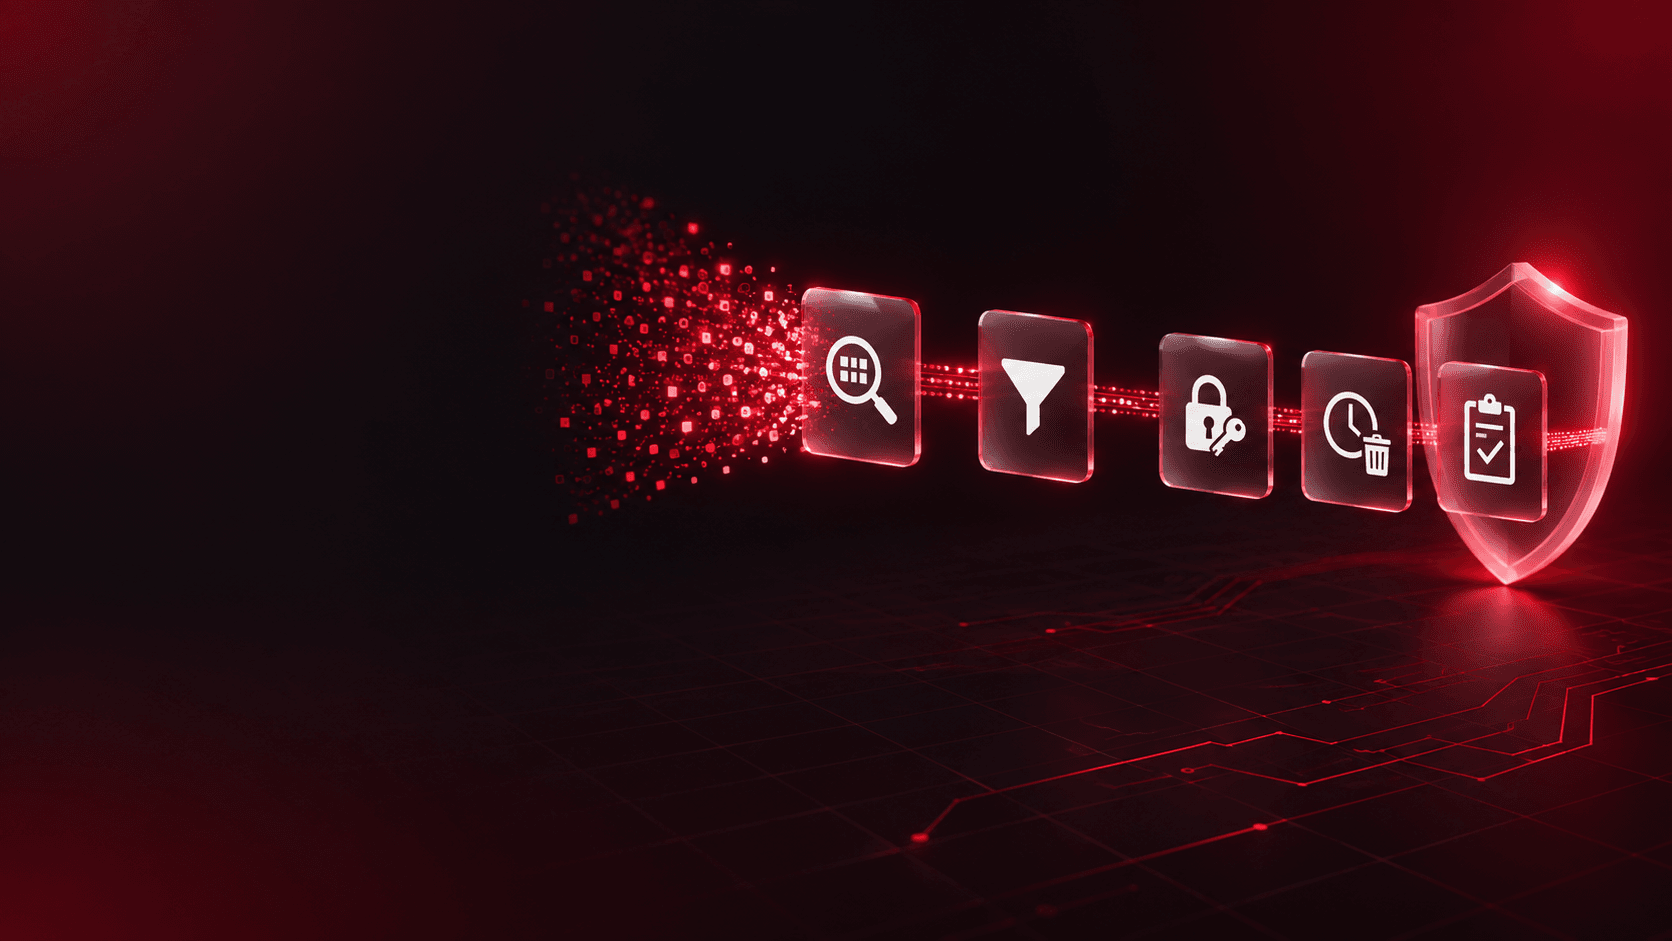
Step 1: Identify the Data Being Collected
Start by understanding what personal data the solution collects, where it flows and why it is required. I ask:
What personal data will the system collect, and why?
Where will it be stored and processed?
Will it be shared with other systems or third parties?
BA deliverable: A data inventory or data-flow overview.
Step 2: Minimise Data Collection
The most important question a BA can ask is: Do we really need this information to achieve the business objective?
Imagine a customer registration platform that asks for name, email, phone, location and date of birth. If the service only needs an email address to send notifications, the rest may be unnecessary. Less data means less to protect, store and manage.
BA deliverable: A data-field specification marking required, optional and unnecessary fields, with business justification.
Step 3: Define Access Controls and Security Requirements
Collecting only necessary data is not enough. Decide who can access it and what safeguards are needed, with stakeholders, before development begins. Clarify:
Which user roles need access, and can they view or modify?
Are authentication, authorisation and audit logging defined?
Does sensitive information need extra protection?
For example, an HR application may let authorised HR staff view employee records while restricting everyone else.
BA deliverable: Role-based access requirements and security-related user stories.
Step 4: Establish Retention and Deletion Rules
Personal data should not be kept indefinitely without a valid reason. I have found retention is easily overlooked when teams focus on collection and functionality. Ask:
How long must the data be kept, and are there legal or contractual obligations?
When should it be archived, anonymised or deleted?
How will deletion work across connected systems and backups?
BA deliverable: A retention and deletion requirements document.
Step 5: Validate and Document Privacy Requirements
I believe a requirement is only useful when the team can check whether it has been met. Instead of writing “Only authorised users should access customer records,” define acceptance criteria: users without the required permissions are denied access, and access attempts are logged where required.
Then confirm that data collection is limited to its purpose, permissions work as specified, retention rules are implemented, and decisions and open risks are documented. Where the processing warrants it, bring in privacy, legal and security specialists for a formal review.
BA deliverable: Validated requirements, acceptance criteria and test evidence.
Common Mistakes to Avoid
Treating Privacy as a Testing-Stage Activity
Privacy belongs in discovery and design, not only in testing.
Collecting Data Without a Clear Purpose
Every data field needs a justified business need.
Ignoring the End of the Data Lifecycle
Retention and deletion matter as much as collection and storage.
Build Privacy into the Process, Not Around It
I think successful business analysis is about more than meeting functional requirements. Business Analysts can make a real difference by asking the right questions early and turning privacy expectations into clear, testable requirements.
Responsible data protection begins long before a product reaches its users. It begins when we decide what information we need, why we need it and how we will protect it.
Better requirements. Safer data. Greater trust.
FAQs
- What is Data Protection by Design?
It is an approach that builds privacy into a product, process or system from the earliest stages of planning, rather than adding it after the solution is built.
- What does a Business Analyst do in data protection?
A BA identifies what personal data a solution needs, challenges unnecessary collection, defines access and retention requirements, and turns privacy expectations into testable acceptance criteria.
- When should privacy be considered in a project?
From discovery and requirement gathering onwards. Fixing privacy at the requirements stage is far cheaper than redesigning a built system.
Comments
0 comments
No comments yet
Be the first to add something to this.
Leave a comment